Release Readiness for the National Data Library: Six Checks Before a Public Dataset Leaves the Estate
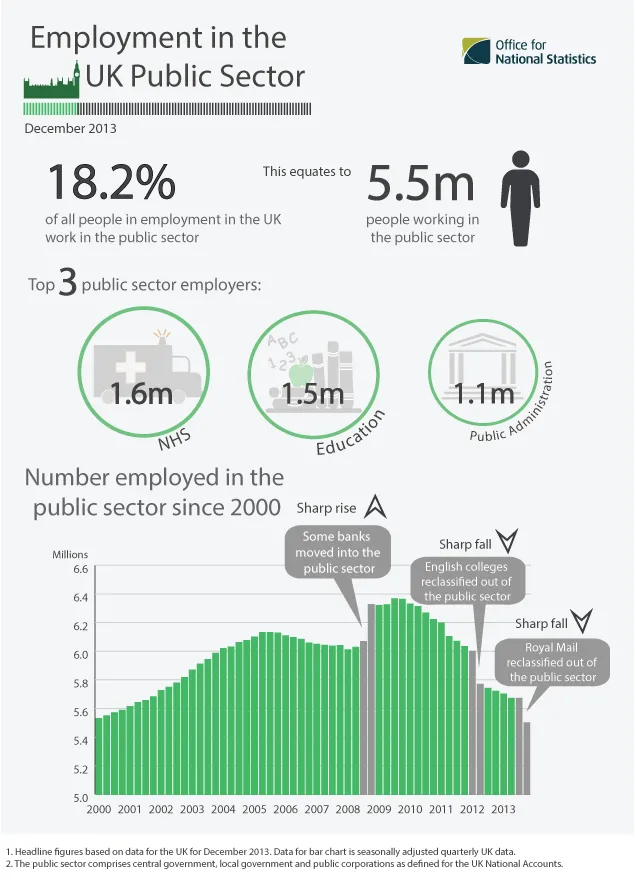
Photo: Office for National Statistics, OGL v1.0, via Wikimedia Commons
The National Data Library is often described in terms of access: researchers, innovators and analysts gaining controlled use of public sector data. For the organisations asked to contribute, however, the more demanding question sits earlier in the process. Before a dataset can be shared safely, the contributing body must be able to explain what it holds, why it may release it, what has been removed or protected, who may use it and on what terms, and who made the release decision. A data-sharing agreement is necessary, but it is not a substitute for that evidence.
This framework proposes a six-point readiness review for UK public bodies preparing contributions to the National Data Library. It is designed as a gate before release, not an obstacle after it. The aim is to make the contribution defensible, repeatable and proportionate to risk.
1. Metadata that supports reuse, not just discovery
A catalogue entry is not a governance control unless it tells the recipient enough to use the data responsibly. Release-readiness should begin with a metadata test covering provenance, definitions, units, collection method, geographic coverage, time period, update frequency and known quality limitations. For each field, the contributing organisation should be able to state whether values are mandatory, derived, estimated or missing by design.
Quality flags matter as much as descriptive labels. A dataset that is suitable for trend analysis may be unsuitable for case-level decisions. A dataset that is complete for England may be misleading if presented as UK-wide. The metadata should also record disclosure-control markings, retention constraints and any conditions attached to reuse. If the library user cannot distinguish a provisional figure from a final one, the metadata has failed its first governance purpose.
2. Lawful basis and purpose mapping at the point of contribution
Public bodies should not treat lawful basis as a single sentence in a privacy notice. The review should map the legal basis for holding the data, the basis for sharing it with the library, and the basis on which each permitted access purpose relies. Where a statutory gateway exists, the relevant provision should be identified. Where public task is relied upon, the mapping should show how the intended reuse connects to the contributing body's functions and the library's remit.
Roles and responsibilities require equal clarity. Is the contributing organisation a controller, a joint controller or a processor in relation to the library copy? Who answers a subject access request or a complaint about misuse? What does the data protection impact assessment say about re-identification risk and onward access? These questions should be answered before the first transfer, not reconstructed during an incident. A purpose map that is broad enough to cover every possible research use is usually too broad to be meaningful.
3. Sensitive-data redaction and residual-risk testing
Redaction is often imagined as the removal of names and addresses. In practice, the greater risks frequently sit in combinations: small geographic areas, rare conditions, unusual dates of birth, free-text fields, operational notes and linked datasets that become more disclosive together than apart. The readiness review should require evidence of disclosure control beyond direct identifiers, including suppression rules for small counts and a documented approach to pseudonymisation where it is used.
Residual-risk testing should be proportionate but independent of the team that prepared the extract. A second reviewer should ask whether a motivated user could infer an individual from the released fields, whether the same information is available elsewhere, and whether the proposed access tier changes the risk calculation. Redaction that has not been tested is an assertion, not a control. The review should record the test performed, the findings and the decision to proceed or rework.
4. Access-tier design tied to risk, not convenience
Access tiers should follow from the sensitivity of the data and the assurance available about the user. A public open tier, a safeguarded tier and a controlled tier may be appropriate, but the labels are less important than the rules attached to them. Each tier should specify eligibility, accreditation, training, technical controls, permitted purposes, output checking and audit arrangements.
A common weakness is to place a dataset in a lower tier because the higher tier is slower to operate. The readiness review should challenge that temptation. If the organisation cannot describe the controls that apply at each tier, or cannot evidence that users have been accredited before access, the tier design is incomplete. The library may provide the platform, but the contributing body remains accountable for the conditions under which its data enters it.
5. Commercial confidentiality and third-party rights
Public sector data is not automatically free of third-party interests. Contracts, licences, database rights, copyright, confidentiality obligations and supplier terms may constrain what can be shared or how it can be reused. The review should identify any data supplied by contractors or partners, any restrictions on onward disclosure, and any commercial information that could harm a supplier or distort a market if released.
Freedom of information and transparency expectations should be considered alongside confidentiality claims. A blanket assertion of commercial sensitivity is rarely sufficient. The contributing organisation should record the specific harm contemplated, the clause or legal basis relied upon, and the period for which the restriction is intended to apply. Where possible, the release should be designed to separate open elements from restricted ones rather than withholding an entire dataset.
6. Accountable release authority and a durable audit trail
Finally, the review should identify the person or role accountable for releasing the dataset. A committee may advise, and legal or data protection teams may assure, but accountability should be named. The decision record should capture the dataset version, the purpose map, the redaction and testing evidence, the access tier, any restrictions, and the date of review. It should also state how the contribution can be withdrawn or amended if circumstances change.
This record is what allows the organisation to answer questions later: why this dataset, why this version, why this tier and why this decision. It also supports consistency when staff move on. A release authority without an audit trail is a signature; a release authority with an audit trail is a governance control.
A gate, not a tollbooth
The National Data Library can create substantial public value, but that value depends on trustworthy contributions. The six checks above are intended to make release readiness visible and reviewable. They should be completed before a dataset leaves the estate, and they should be revisited when the data, the law, the access model or the risk environment changes. Contributing organisations that treat the library as a destination may find themselves answering avoidable questions later. Those that treat it as a controlled release programme will be better placed to share confidently, and to explain why.